Building a GDPR-compliant business website has two main jobs: help the right person contact your business and make that person feel safe doing it. Those goals do not conflict. In fact, a clear privacy experience can remove hesitation and improve the quality of inquiries.
A GDPR-compliant business website collects only useful information, explains why it is needed, uses an appropriate lawful basis, protects every handoff, and gives people meaningful control. It does not need frightening pop-ups or forms filled with legal jargon.
What Makes a GDPR-Compliant Business Website?
Short answer: A compliant website explains its data practices, chooses a lawful basis for each purpose, limits collection, manages cookies and vendors responsibly, protects personal data, and provides a practical route for privacy requests.
The European Commission identifies principles, lawful grounds, transparency, security, breach responsibilities, and data-subject rights as important parts of business compliance. That makes GDPR a website-and-workflow issue, not simply a privacy-policy issue.
Map the GDPR-Compliant Business Website Data Journey
Start with what happens after someone selects “Request a quote.” The information may move from your website to a form service, email provider, lead management system, calendar tool, analytics platform, sales inbox, and backup system. Each handoff deserves a clear purpose and an appropriate security decision.
Create a simple inventory:
- What information is collected?
- Why is each field needed?
- Where is it stored, and who can access it?
- Which vendors process it?
- When is it deleted or reviewed?
Furthermore, this exercise exposes unnecessary questions. For example, your team only needs a visitor’s name, business email, company, and project summary for a first inquiry. Asking for a full address, phone number, budget, job title, and ten other details can reduce completion without helping the first conversation.
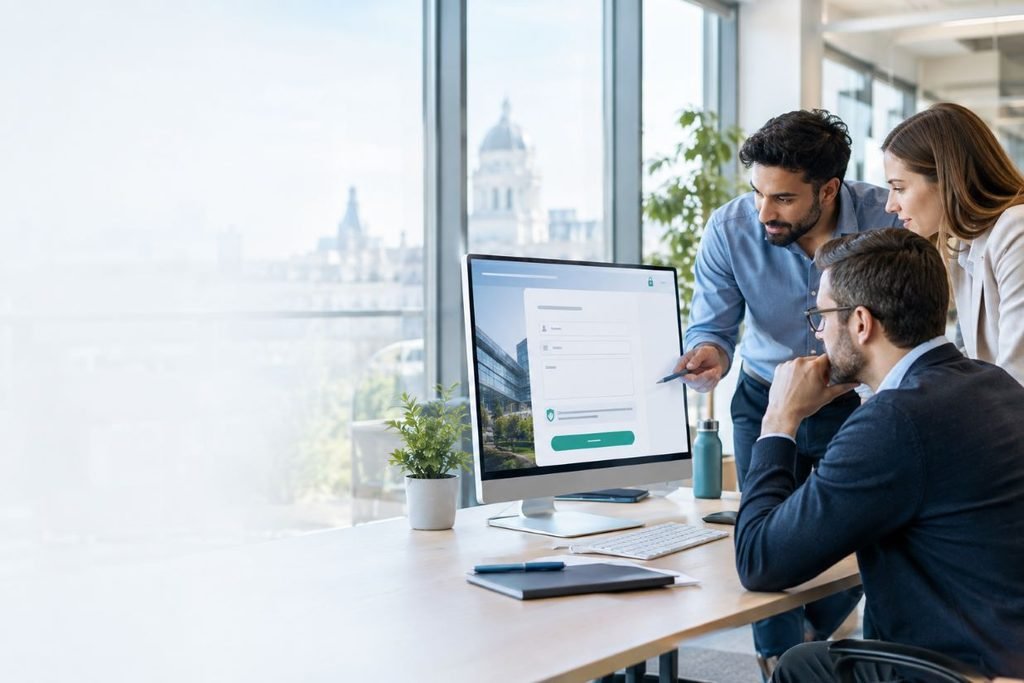
A privacy-first lead form should make the next step clear without hiding how submitted information will be used.
Choose the right lawful basis for each purpose.
Direct answer: Do not use one generic consent checkbox for every activity. The correct lawful basis depends on the purpose, context, and applicable rules.
Clearly, responding to a person who requests a quote is different from sending that person a promotional newsletter. Keep the enquiry process focused on the requested service. If you want to offer marketing updates, provide a separate, optional choice and explain it plainly.
The European Data Protection Board describes valid consent as freely given, specific, informed, and expressed through a clear action. Wording such as “By continuing, you agree to everything” is not a good substitute for a precise explanation.
A practical form message might say:
“We will use these details to respond to your project inquiry. See our privacy notice for information about storage, providers, retention, and your rights.”
In addition, your team should keep the full notice current, easy to open, and clear for real website visitors.
Design Forms for a GDPR-Compliant Business Website
A GDPR-friendly lead form can be short, persuasive, and accessible. Ask for the minimum information needed to provide the next useful step. Use meaningful labels, clear error messages, keyboard navigation, readable contrast, and a mobile-friendly layout.
Furthermore, do not bundle optional marketing permission into the enquiry action. Instead, use an unticked checkbox with a separate explanation, which visitors understand much faster than a preselected option. If a lead management system or scheduling platform receives the data, describe relevant processing and vendor relationships in the privacy notice.
The best conversion test is not “How many fields can we remove?” It is “What is the smallest amount of information needed for a useful response?” Many service businesses can use a two-stage journey: a short inquiry first, followed by a tailored discovery call.
Clear explanations and fewer unnecessary fields can support both privacy and lead conversion.
Handle cookies, analytics, and tracking carefully.
Short answer: Explain non-essential cookies and similar technologies before using them where consent is required, and make the choice clear and reversible.
The ICO explains that organizations should tell people what cookies do and why they are used and obtain active consent where required. Strictly necessary technologies may be treated differently from optional analytics and advertising tools, but “helpful to the business” does not automatically mean “strictly necessary.”
Keep the first layer of a cookie banner concise. Offer understandable categories, avoid manipulative button design, and do not load optional tags before the visitor has made the required choice. Review your scripts regularly; if a tag has no clear business purpose, remove it.
Therefore, analytics should answer practical questions, such as which service page produces qualified enquiries. They do not need to capture every interaction with identifiable detail. A privacy-respecting measurement plan can still report form completion, source performance, and conversion quality.
Protect Your GDPR-Compliant Business Website and Data
Privacy copy cannot compensate for exposed form data, weak administrator accounts, outdated software, or an unsecured lead management system. Your website project should include encrypted connections, strong authentication, role-based access, updates, secure backups, and a documented incident process.
Review vendors that process personal data on your behalf, including access, contracts, storage, transfers, and deletion. The European Commission includes security and processor responsibilities within the business compliance picture. Limit lead exports, review access regularly, and remove accounts when team members leave.
A practical GDPR website checklist
| Website area | Risk to check | Better implementation |
| Lead form | Unnecessary fields | Collect only what the next step needs. |
| Marketing checkbox | Bundled or unclear permission | Use a separate, optional explanation. |
| Cookie banner | Optional tags fire early. | Load them only after the required choice. |
| Privacy notice | Generic or hidden information | Link a clear, current notice beside the form. |
| Lead management system | Too many people see leads. | Use roles, access reviews, and retention rules. |
| Performance | Consent tools slow the page. | Test mobile speed and Core Web Vitals. |
Keep the website fast, accessible, and search-friendly.
A GDPR-compliant website still needs strong technical SEO. Consent managers, tag systems, chat widgets, and third-party scripts can affect page speed. Load optional tools conditionally, test the form on real mobile devices, and monitor Core Web Vitals alongside conversions.
Accessibility matters too. Every field should have a useful label, the form should work with a keyboard, and error messages should explain how to recover. An accessible form reduces friction for everyone, not only people using assistive technology.
For AI-driven search, place direct answers under descriptive headings, support factual claims with authoritative references, and make the page genuinely useful. Google’s people-first guidance favors content created to help visitors rather than pages designed only to manipulate rankings. Use Article, Service, Organization, and BreadcrumbList structured data only when it accurately reflects visible content. Add FAQ schema only for visible questions and answers and only where current Google guidance supports it.
How to review the website before launch
Submit every form with test data and document where it goes. Inspect cookies before and after consent, check the privacy notice on mobile, test keyboard navigation, and confirm that marketing permission is stored separately where appropriate. Then measure completed inquiries, qualified leads, form abandonment, and source-level performance.
Final takeaway
A GDPR-compliant business website does not lose leads because it respects visitors. It loses leads when privacy is confusing, the form is demanding, the site is slow, or follow-up feels uncertain.
As a result, when you map the data journey, collect less information, explain practices clearly, and secure every handoff, privacy and conversion work together seamlessly. That is how privacy and conversion work together.
Frequently Asked Questions About GDPR-Compliant Business Websites
Does every website form need a consent checkbox?
Not necessarily. The answer depends on the purpose and lawful basis. For instance, your team should not treat an enquiry response and an optional newsletter as the same activity. Therefore, document your reasoning and obtain professional advice for your situation.
Can a GDPR-friendly website still use analytics?
Often, yes, but the tool, settings, consent requirements, and national rules matter. Review what it collects, when it runs, and whether a less intrusive method can answer the same question.
What should a privacy notice explain?
It should cover relevant purposes, data categories, lawful bases, processors, retention, rights, and contact details. A privacy professional should confirm the final notice.
References
[1] European Commission—Information for business and organizations
[2] European Data Protection Board — Guidelines 05/2020 on consent
[3] ICO — Cookies and similar technologies
[4] Google Search Central—Creating helpful, reliable, people-first content